RED directive and EN 18031: what applies until December 2027, and after
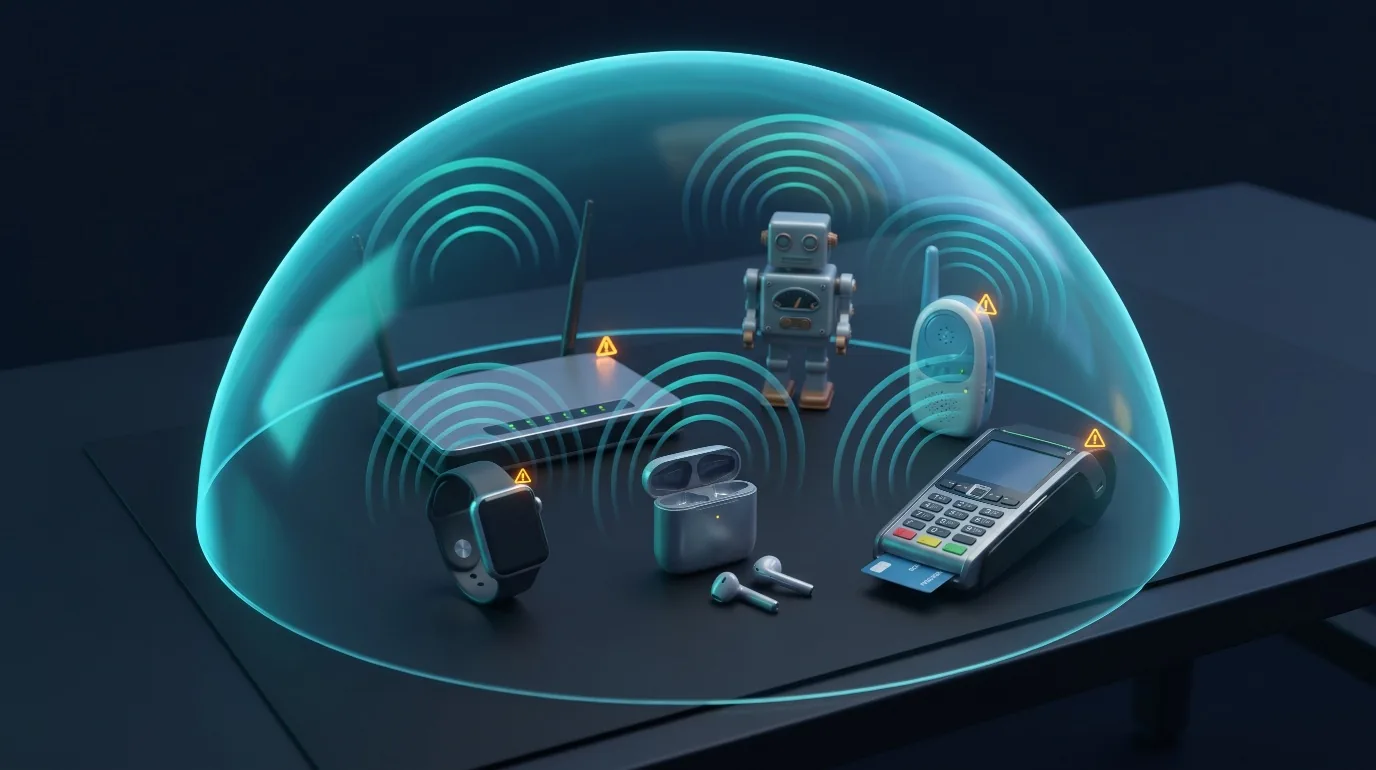
Many product teams are preparing for the Cyber Resilience Act for 2027, thinking they have time. They forget that a cybersecurity obligation already applies, since August 1, 2025, to almost every wireless connected device sold in Europe. It comes from the RED directive.
The two texts are often confused. Here is what each requires, how they fit together, and what a manufacturer must do before the switchover.
The RED directive and its cybersecurity part
Directive 2014/53/EU, known as the RED (Radio Equipment Directive), governs the placing on the market of radio equipment: Wi-Fi, Bluetooth, cellular, LoRa, Zigbee. It is a condition for CE marking.
Its Article 3(3) provided for cybersecurity requirements that long remained inactive. Delegated Regulation (EU) 2022/30 activated them. After a one-year postponement, they have applied since August 1, 2025.
Three requirements
| Article | Requirement | Equipment concerned |
|---|---|---|
| 3(3)(d) | Do not harm the network or misuse its resources | Radio equipment able to communicate over the Internet, directly or indirectly |
| 3(3)(e) | Protect personal data and privacy | Equipment processing personal, traffic or location data, toys, childcare equipment, wearables |
| 3(3)(f) | Protect against fraud | Equipment enabling the transfer of money or value |
Some sectors already covered by their own regulations are excluded, notably medical devices, civil aviation and automotive.
In France, market surveillance of radio equipment is carried out by the ANFR.
EN 18031: the harmonized standard
To demonstrate compliance, manufacturers rely on the EN 18031 series, published by CEN and CENELEC in 2024:
- EN 18031-1 for network protection
- EN 18031-2 for personal data protection
- EN 18031-3 for fraud protection
These standards review, mechanism by mechanism, what a product must implement: access control, authentication, secure updates, secure storage, secure communications, key management, resilience, logging, absence of known exploitable vulnerabilities.
They were cited in the Official Journal of the European Union in January 2025. A product that complies with them benefits from a presumption of conformity, which allows the manufacturer to proceed by self-assessment.
The restrictions, often overlooked
The citation in the Official Journal comes with restrictions. In some cases, applying the standard is not enough to obtain the presumption of conformity, and a notified body becomes necessary again:
- when the product allows the user not to set or not to use a password
- for toys and childcare equipment, when parental access control is not guaranteed
- for equipment handling financial assets, on the assessment criteria for secure updates
The first case concerns a large number of consumer products. A device that works without a password, or with a default password the user is not forced to change, falls outside the scope of the presumption.
How it relates to the Cyber Resilience Act
This is where confusion is most frequent.
The Cyber Resilience Act covers, in its Annex I, everything addressed by the three RED requirements, and adds obligations over the whole lifecycle. To avoid two overlapping regimes, the European Commission adopted Delegated Regulation (EU) 2026/339, published on April 29, 2026. It repeals Regulation 2022/30 as of December 11, 2027, the date the CRA fully applies.
| Period | Regime applicable to connected radio equipment |
|---|---|
| Before August 1, 2025 | No cybersecurity requirement under the RED |
| From August 1, 2025 to December 10, 2027 | RED requirements 3(3)(d), (e), (f), with EN 18031 |
| Since September 11, 2026 | In addition: CRA reporting obligations |
| From December 11, 2027 | Full CRA requirements, the RED cybersecurity part disappears |
Three practical consequences.
Waiting for the CRA is not an option. Every unit placed on the market until December 10, 2027 must meet the RED requirements.
The CRA reporting obligations already apply to radio equipment. RED compliance does not exempt you from them. Details are in our article Cyber Resilience Act: what has applied since September 11, 2026.
EN 18031 is not a harmonized standard under the CRA. The work done can largely be reused for the technical requirements, but it will not give a presumption of conformity with the CRA. New standards are being drafted for that purpose.
What the CRA adds
A product compliant with EN 18031 has gone a good part of the way on the security of the product itself. It still lacks what the RED does not require:
- a software bill of materials (SBOM)
- a vulnerability handling process and a coordinated disclosure policy
- a stated support period, with security updates throughout its duration
- reporting of exploited vulnerabilities and severe incidents
- a documented risk assessment covering the whole lifecycle
In other words, the RED looks at the product on the day it is placed on the market. The CRA also looks at the years that follow.
What to do now
- Check that your current products comply with the RED. The obligation is more than a year old. If the analysis has not been done, it is the priority.
- Reread the restrictions. If one of them applies, self-assessment is not enough.
- Test, don’t just document. The EN 18031 standards describe mechanisms. Only a test shows that they work on the actual product, debug interfaces and updates included.
- Build the CRA delta now: SBOM, vulnerability handling, support period.
- Avoid doing the work twice. Structure the RED technical file so that it can be extended to the CRA.
Where training plays a role
The RED and CRA requirements are written in terms of objectives. Translating them into design choices requires knowing what an attacker actually does with an open debug interface, a secret in a firmware or an unsigned update.
The DVID CRA path covers the Annex I requirements one by one, with a demonstration on real hardware for each. It is described in our training programs. For consumer products, see also our article on the ETSI EN 303 645 standard.
Frequently asked questions
My product has had CE marking since 2023. Am I concerned?
Yes, for every unit placed on the market since August 1, 2025. Compliance is assessed when each unit is placed on the market, not on the date of the first certification.
Is EN 18031 mandatory?
No. It is the most direct way to demonstrate compliance. A manufacturer can take another route, through a notified body.
Will compliance have to be redone in December 2027?
For units placed on the market from that date, compliance will be demonstrated under the CRA. The security mechanisms already in place remain valid. The lifecycle obligations are added to them.
Further reading
Contact us: https://dvid.eu/#contact
Access the platform: https://experience.dvid.eu
Follow our news: https://www.linkedin.com/company/dvid/
Sources
- Directive 2014/53/EU (RED): https://eur-lex.europa.eu/eli/dir/2014/53/oj
- Delegated Regulation (EU) 2022/30: https://eur-lex.europa.eu/eli/reg_del/2022/30/oj
- Implementing Decision (EU) 2025/138, citation of the EN 18031 standards with restrictions
- Delegated Regulation (EU) 2026/339, repeal of Regulation 2022/30 as of December 11, 2027
- Regulation (EU) 2024/2847 (Cyber Resilience Act): https://eur-lex.europa.eu/eli/reg/2024/2847/oj