Our training programs: build your skills in embedded and IoT cybersecurity
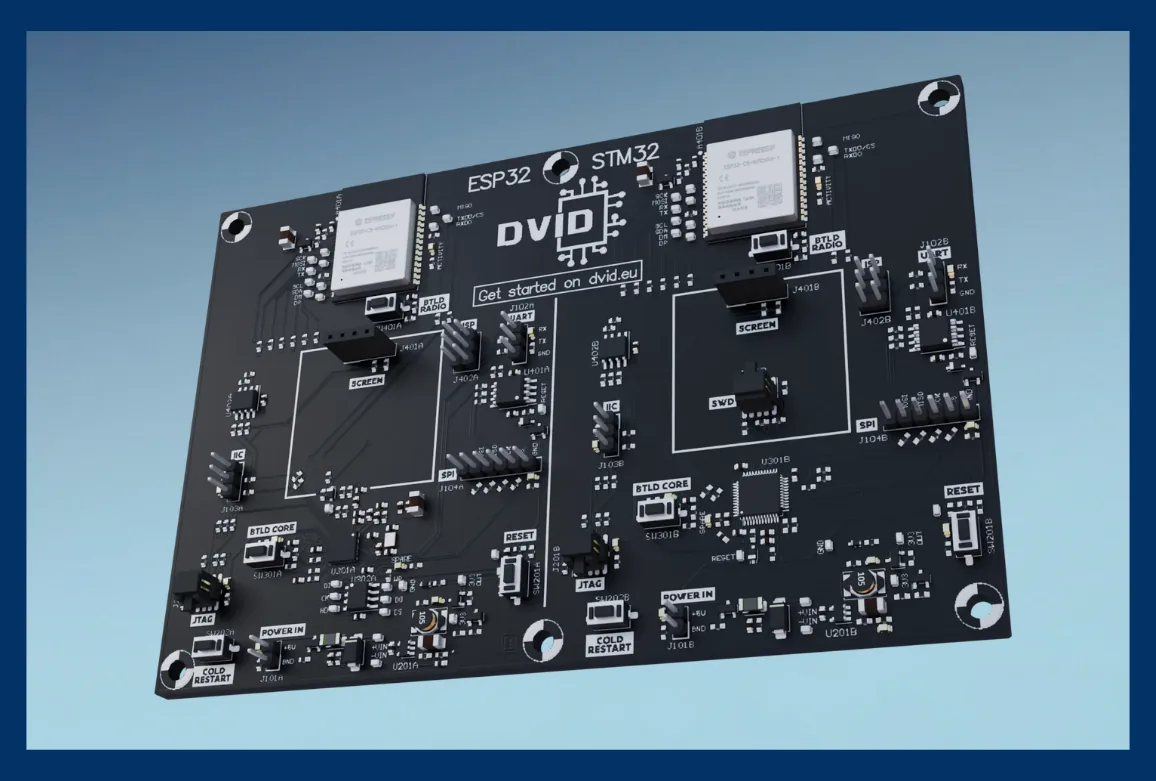
Connected device cybersecurity cannot be improvised. At DVID, we offer three 100% online training paths, designed to get straight to the point: practice, real hardware, field scenarios.
Discover the content of each program below. The full syllabi are available as PDF downloads (in French) at the end of each section.
IoT Security — Level 1
Understand and exploit IoT vulnerabilities
21 modules · 21h
This path immerses you in the reality of IoT security. You learn to map attack surfaces, exploit hardware and cloud vulnerabilities, analyze a firmware and propose remediations — all on real hardware.
Who is it for?
Embedded developers, pentesters, security engineers, CISOs, IoT product managers.
What you will learn
The path covers 4 categories across 21 progressive modules:
Hardware (12 modules) — Getting started with the DVID board, UART and I2C protocols, firmware secret extraction, baud rate, datasheets, WiFi sniffing, firmware signature bypass…
Middleware (2 modules) — MQTT protocol, exploiting misconfigured policies.
Cloud (7 modules) — Exposed tokens, overly verbose APIs, CSRF, weak PKI, error handling, arbitrary download, predictable identifiers.
Assessment
Each module is validated by a flag (technical proof). A final challenge combines several vulnerabilities. A certificate of attendance + DVID certification (digital badge) are awarded.
Cyber Resilience Act (CRA) — Level 1
Understand the European CRA requirements in practice
22 modules · 12h
The CRA comes into force in September 2026. This path lets you concretely master the 22 requirements of Annex I, illustrated by demonstrations on the DVID platform.
Who is it for?
Compliance managers, IoT project managers, CISOs, quality and certification engineers.
What you will learn
Part I — Essential cybersecurity requirements (14 modules)
Security level appropriate to the risks, no known vulnerabilities, secure default configuration, updates, access protection, confidentiality, integrity, data minimization, availability, attack surface limitation, monitoring, secure data deletion…
Part II — Vulnerability handling (8 modules)
SBOM, fast vulnerability remediation, regular testing, coordinated vulnerability disclosure (CVD), secure distribution of updates, free distribution of patches…
Assessment
Validation quiz (70% pass mark) + certificate of completion.
IEC 62443 — Industrial systems security
Cybersecurity requirements for industrial IoT components
8 modules · 8h
This path covers the 7 Foundational Requirements of the IEC 62443-4-2 standard — the reference for industrial systems cybersecurity. Each requirement is illustrated by concrete scenarios on the DVID board or in a virtualized environment.
Who is it for?
Automation engineers, OT/ICS security managers, industrial integrators, certification managers.
What you will learn
The IEC 62443 standard is the reference for industrial systems cybersecurity. This 8-module path covers all 7 Foundational Requirements of IEC 62443-4-2.
You will learn to interpret and apply the standard's requirements: identification and authentication, access control, data integrity and confidentiality, flow segmentation, security event detection and protection against traffic analysis. Each requirement is illustrated by concrete scenarios on the DVID board or in a virtualized environment.
Assessment
Validation quiz (70% pass mark) + certificate of completion.
Common to all our trainings
100% online, 100% self-paced. You progress at your own pace on experience.dvid.eu, 24/7. No scheduled sessions, no virtual classroom.
Automated tracking. Your progress is visible in real time through the Skill Radar. Inactivity alerts and follow-ups from the teaching contact if needed.
Responsive support. Email (contact@dvid.eu) and Discord, answer within 48 business hours.
Ready to take action?
Discover the platform at experience.dvid.eu
Contact us: contact@dvid.eu
Connected device security starts here.